On September 15, 2026, the XRP ecosystem experienced a significant security incident: more than 2 million XRP tokens were transferred from 1,552 wallets within two hours. The XRP Ledger protocol itself was not breached. However, the event has raised questions about the safety of wallet management software. The DCENT App Wallet has emerged as a central focus in the ongoing investigation.
The rapid succession of unauthorized transfers has prompted both regulatory and institutional scrutiny. With no evidence of a protocol-level hack, attention is turning to software vulnerabilities and user practices. This highlights the critical distinction between blockchain security and the tools users rely on to safeguard their assets.
- Key points about XRP:
- Over 2 million XRP were siphoned from 1,552 wallets on September 15, 2026, without compromising the core XRP Ledger protocol.
- The DCENT App Wallet is under investigation for software-related vulnerabilities, with no definitive cause established yet.
XRP: the breach that shifted the regulatory landscape
The confirmed mass drainage of 1,552 XRP wallets in under three hours has become a regulatory turning point. Blockchain analysis verified that 2,009,321 XRP were withdrawn and funneled to two collector addresses in a highly coordinated operation. The incident did not exploit any weakness in the XRP Ledger protocol; instead, it exploited vulnerabilities likely linked to the DCENT App Wallet environment.
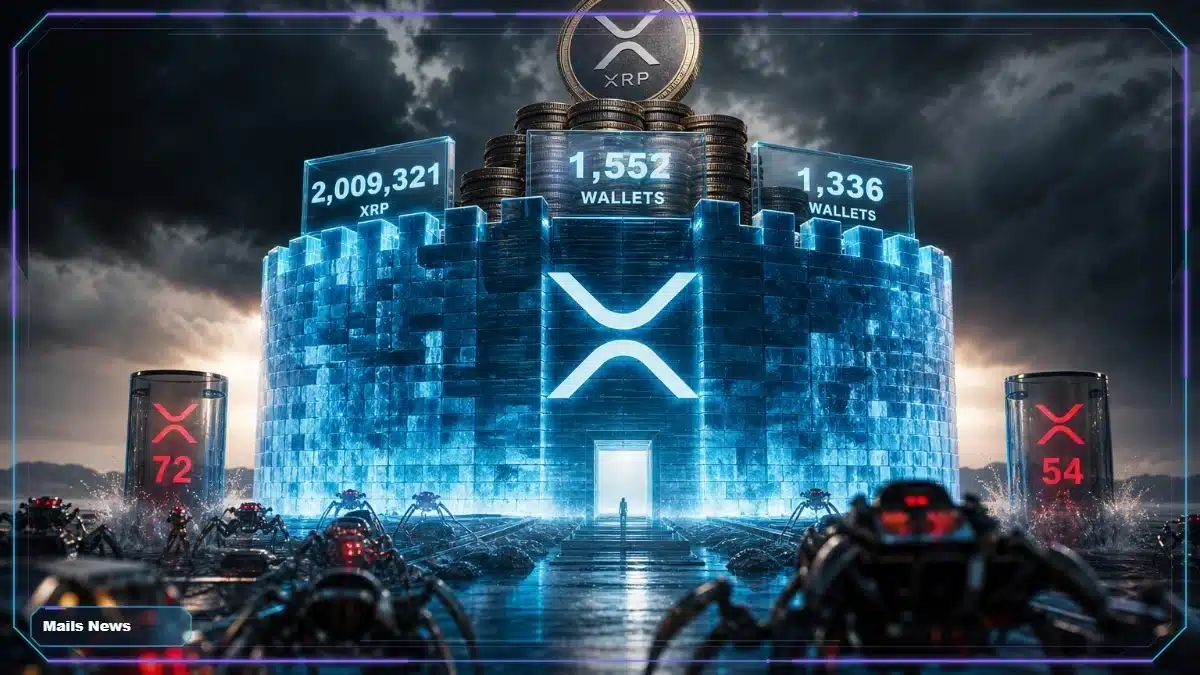
XRPL.Data reveals the operation occurred in two waves. First, 204 wallets were drained. After a technical pause, an additional 1,336 wallets were affected. The largest accounts, each holding more than 42,000 XRP, were targeted with dedicated tools, indicating the methodical preparation and automation behind the event. Failed attempts—72 in the first wave and 54 in the second—were primarily due to protocol-enforced minimum reserves, not flaws in the core ledger. The attack order followed wallet creation dates, suggesting a precompiled list was used.
What the evidence and figures show
Forensic analysis confirms there was no compromise of the XRP Ledger protocol. Investigators are focusing on the DCENT App Wallet. Most affected users had previously entered recovery phrases or signed transactions using versions prior to 8.1.0. DCENT acknowledged receiving reports of unauthorized transfers on September 16 and is cooperating with law enforcement and cybersecurity experts.
DCENT’s published risk criteria show users may be vulnerable if they entered their recovery phrase into the DCENT App Wallet. The risk increases if they used it for actions such as NFT management or decentralized application interactions. The risk may not be exclusive to XRP; other networks including Bitcoin, Ethereum, Tron, and EVM-compatible chains could be affected under similar conditions.
On-chain tracking as of September 16 at 14:00 UTC showed 1,808,974 XRP remained in four wallets controlled by the operator. Approximately 236,000 XRP had reached exchanges or bridges. Although blockchain transparency allows precise monitoring of these movements, it does not clarify how private keys were compromised. DCENT has recommended that users who entered their recovery phrase into the app generate a new seed. They should transfer assets to a fresh wallet, rather than restoring the old phrase on another device.
Market response was subdued. Trading volumes on major exchanges stayed within normal ranges, and no sharp price drop occurred. This indicates the market viewed the event as isolated rather than systemic.
What to watch next for XRP and wallet security
The next critical milestone for XRP’s regulatory and institutional environment will be the disclosure of the technical findings from DCENT and partner cybersecurity teams. This will determine whether a specific software vulnerability or a broader operational risk is implicated. The outcome could influence both wallet provider practices and user security protocols across the ecosystem.
Users affected by the incident are urged to monitor official DCENT communications, follow recommended security measures, and be cautious with recovery phrase handling. A central uncertainty remains: the precise mechanism of compromise has yet to be identified. The potential for fund recovery depends on the ability to freeze assets across exchanges and bridges. Regulatory responses may intensify if the vulnerability is found to affect multiple digital asset ecosystems.
For now, the incident underscores that while blockchain protocols can remain secure, the tools and habits around them are often the weakest link. The first reliable sign of resolution will be the publication of a comprehensive investigation report or a successful freeze or clawback of drained tokens.
FAQ: XRP, DCENT App Wallet, XRPL
Which verified fact changes the current picture for XRP? Blockchain analysis verified that 2,009,321 XRP were withdrawn and funneled to two collector addresses in a highly coordinated operation. What concrete consequence does that fact have for XRP? Which next milestone, date or uncertainty should be verified for XRP?
Forensic analysis confirms there was no compromise of the XRP Ledger protocol. Investigators are focusing on the DCENT App Wallet. Most affected users had previously entered recovery phrases or signed transactions using versions prior to 8.1.0. DCENT acknowledged receiving reports of unauthorized transfers on September 16 and is cooperating with law enforcement and cybersecurity experts..
Which next milestone, date or uncertainty should be verified for XRP? The next critical milestone for XRP’s regulatory and institutional environment will be the disclosure of the technical findings from DCENT and partner cybersecurity teams. Blockchain analysis verified that 2,009,321 XRP were withdrawn and funneled to two collector addresses in a highly coordinated operation.
Disclaimer: This article is for informational purposes only and does not constitute investment advice. Cryptocurrencies are volatile assets. Always conduct your own research before making financial decisions.